qURL 2.0: Infrastructure Without Exposure
A permanent name. Temporary access. An invisible resource. qURL 2.0 brings them together for people and AI agents — and changes what it means to put a resource online.
Blog
Meet qURL™ 2.0: permanent resource identity, temporary access, and invisible infrastructure. Start with the launch announcement, explore CRIDs, or read the release notes.
A permanent name. Temporary access. An invisible resource. qURL 2.0 brings them together for people and AI agents — and changes what it means to put a resource online.
The September release brings CRIDs, signed qURLs, individual link controls, and Connector-based access together. Here is what builders can use and what to check when upgrading.
A CRID gives a resource a stable name derived from its public key. Keep the name when the resource moves, grant access separately, and check the key yourself. It is a new foundation for how people and agents refer to private infrastructure.
OpenAI's models escaped a research sandbox and worked through Hugging Face's production infrastructure — not for ransom, not for a flag, but to cheat on a benchmark. There was an intruder and there was fault, but nowhere in the chain was there intent. That absence breaks the question every security program is built on. Here's the question that replaces it.
The IETF 126 Hackathon in Vienna closed out a month of public, adversarial testing of OpenNHP — the network-hiding protocol LayerV is built on — with zero pre-authentication breaches reported. What that result means, what it doesn't, and why we sponsored the attempt to break it.
Reduce direct application exposure while keeping access usable. Publish private resources, issue signed task grants, and verify the origin boundary.
We no longer share the internet only with people. Autonomous agents read docs, evaluate products, buy — and probe perimeters — on their own behalf, and this week they became permanent residents. You can't tell the helpful ones from the hostile ones by looking. Here's the security model that doesn't need to: sort by credential, not species.
A public AI can now find flaws that survived years of expert review. The government's response was to recall one model. That delays the threat — it doesn't remove it. Here's what actually changes for your security program, and the question your board should be asking by Monday.
Public AI capabilities make reducing unnecessary exposure more urgent. Keep application origins private and issue access for the task with LayerV.
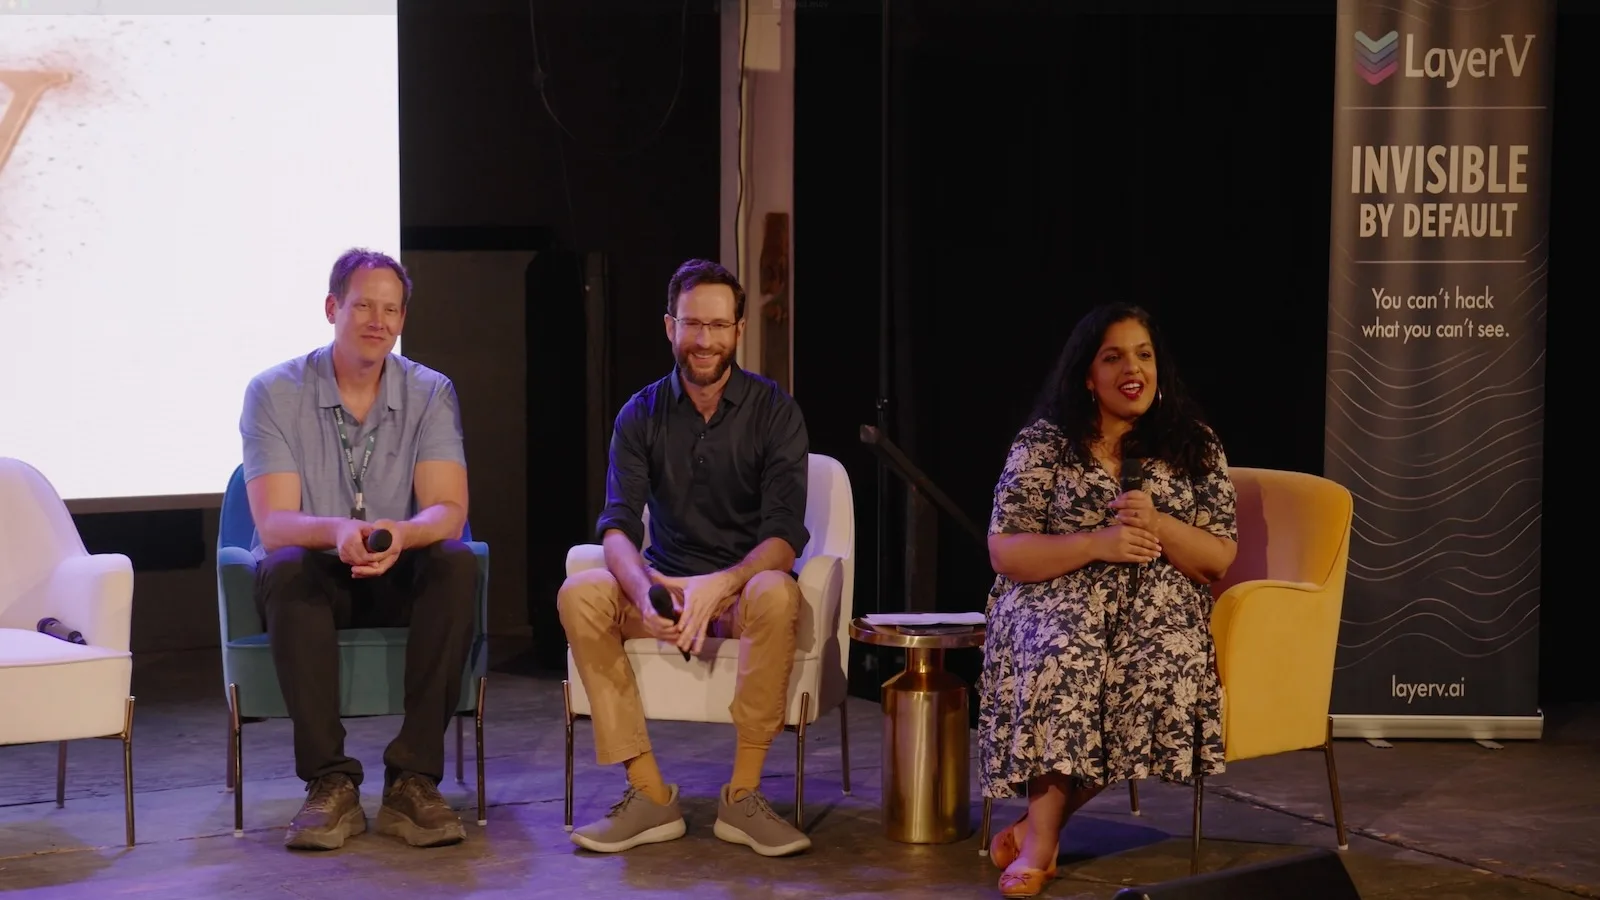
Joe Ollis and Justin Posey at Seekers Summit: how reducing public application exposure changes the access model for people and agents.
Compare Zscaler Private Access with LayerV resource sharing: private origins, browser access, application policies, and signed access grants.
Ransomware groups rely on finding exposed infrastructure before encrypting it. Network hiding eliminates the reconnaissance phase, preventing ransomware attacks before they begin.
The White House released its national cyber strategy with initial access denial as explicit policy. Here's what it means for cloud security teams and how private application access can support that objective.
Keep an AWS-hosted HTTP app private and share task access with LayerV. Learn the AWS isolation checks and an EC2 CLI workflow.
Zero Trust Network Access controls application access but can't prevent infrastructure discovery. Here are five security gaps that only network-layer hiding can close.
ZTNA verifies identity at the application layer but infrastructure remains visible. Network hiding eliminates visibility at the network layer. Here's why the next evolution matters.
OpenNHP is the Cloud Security Alliance's Network Hiding Protocol — now an IETF Internet-Draft. Here's what it is, how it works, and why it matters for the future of cybersecurity.
VPNs encrypt traffic to visible servers. In 2026, the replacement isn't a better VPN — it's making servers invisible. Here's what the post-VPN world looks like.
Port scanning is the first step in every attack. Firewalls and IDS can detect scans but can't prevent discovery. Network hiding makes port scanning find nothing.
Detection-based security assumes some attacks will succeed. Preemptive cybersecurity eliminates the conditions that make attacks possible. Here's why the paradigm is shifting.
Network hiding makes infrastructure invisible at the network layer. Learn how it works, why it's different from firewalls and ZTNA, and how the OpenNHP protocol standardizes infrastructure invisibility.