nginx2root: The Server That Answers Everyone
nginx2root takes an unauthenticated caller from an HTTP/2 frame to root on the host. Patch nginx today, then take the nginx that guards your internal tools off the internet with qURL and OpenNHP.
nginx has one job: answer whoever connects. Today that job became the vulnerability.
Yesterday it was Java4Shell, and the lesson was that the login page didn't matter. nginx2root makes the same point one layer further out. nginx sits in front of the login page. It parses the attacker's bytes before your application, your SSO or your WAF rules get a vote. If an unauthenticated stranger can open a connection to it, they can attempt this exploit.
So patch today. Then decide which of your nginx servers should ever have answered a stranger in the first place.
What Happened
On November 18, 2026, Xint disclosed nginx2root: five memory-safety bugs in nginx and one in the Linux kernel. Each nginx flaw is a separate attack path. Xint demonstrated a chain from an unauthenticated network caller to code execution inside an nginx worker, and from there to root on the host. Xint's technical write-up covers each bug in detail. nginx released fixes the same day.
| CVE | Where | Bug | Exposed when | Affected path since (Xint) |
|---|---|---|---|---|
| CVE-2026-123007 | HTTP/2 flow control | Integer overflow, out-of-bounds heap write | HTTP/2 is on | 1.9.5 (2015) |
| CVE-2026-123633 | HTTP/2 connection draining | Use-after-free | HTTP/2 is on and requests are proxied upstream | 1.19.7 |
| CVE-2026-121810 | HTTP/3 (QUIC) stream creation | Use-after-free | HTTP/3 is on and requests are proxied upstream | 1.25.0 |
| CVE-2026-123634 | DNS resolver with | Use-after-free |
| 1.13.4 for this path; vendor range starts at 0.6.18 |
| CVE-2026-113425 | Mail proxy | Use-after-free | The mail proxy runs with | 0.5.15 per Xint; vendor range starts at 0.5.33 |
| Linux SCTP | Kernel send path | Use-after-free, double free | The SCTP module can load | Kernel 4.15 (2018) |
Every nginx bug runs before authentication. The headline one, CVE-2026-123007, needs nothing more than HTTP/2 on the listening port. Rapid7 rates it CVSS 9.2 and published a proof of concept. Xint describes an integer overflow; Rapid7 describes the unsigned underflow in the window check. Both lead to the same memory corruption.
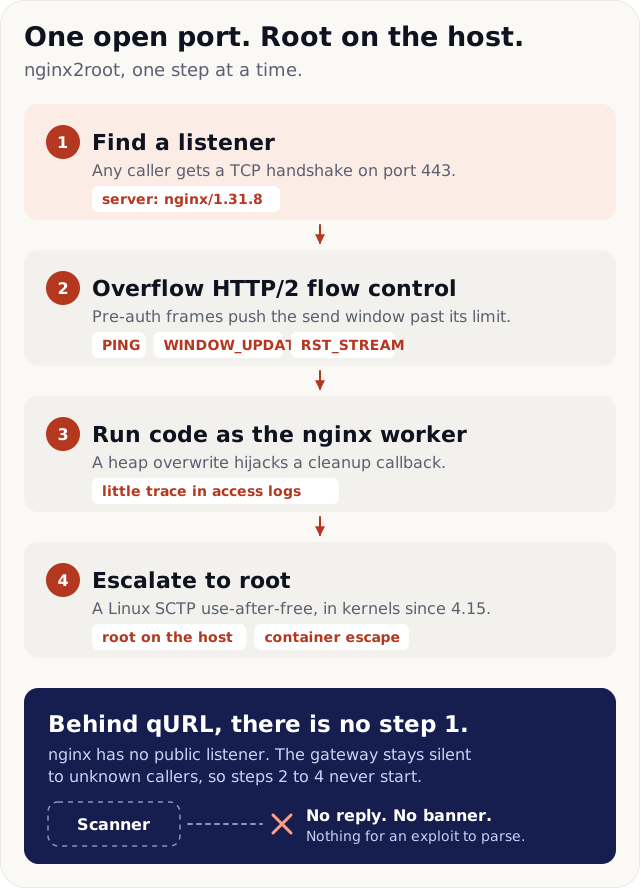
Four details from the disclosure explain why this one is different:
- Eleven years. CVE-2026-123007 has been in every nginx release since HTTP/2 arrived in 2015.
- 56.7 million hosts. Xint reports this Shodan count as of November 10. Of the 11.94 million hosts with an identified version, 98.9% were in the affected range. Version strings alone do not prove exposure: HTTP/2 must be enabled, and packages can include backported fixes.
- Almost no trace. Xint warns that the control frames used for CVE-2026-123007 may leave little evidence in access logs. Check the other indicators in its advisory too.
- Found by machine. Xint reports that its automated scan found four of the nginx bugs without human guidance.
That last point matters most. The same class of tooling that found these bugs is available to the people who want to use them.
Patch nginx Today
Upgrade to nginx 1.31.9 (mainline) or 1.30.7 (stable). For NGINX Plus, check the fixed release for your branch in F5's advisory. nginx hides inside other things, so check the copies in container images, Kubernetes ingress controllers and appliances too. Until every copy is patched, Xint's interim mitigations are: turn off HTTP/2 (
http2 off;on 1.25.1 or later; removehttp2fromlistendirectives on older versions) and HTTP/3 (http3 off;), pointproxy_passat fixed upstream groups instead of request-derived values, and bind mail proxy listeners to loopback. For the kernel half, follow Xint's SCTP mitigations. A modprobe rule does not remove an already loaded module. Restart nginx after the binary update; a configuration reload alone does not replace it. Use Xint's advisory and nginx's security advisories for the details.
Turning off HTTP/2 on a busy site is a performance hit you will feel. That is the trade every team running public nginx is weighing this afternoon.
Most of Your nginx Isn't Your Website
Your marketing site has to answer strangers. That is its job.
Now count the rest. The reverse proxy in front of Grafana. The one in front of Jenkins, Argo and Kibana. The staging environment, the admin panel, the internal API, the vendor portal, and the ingress controller that routes all of it. When these tools sit behind public nginx, the reason is often simple: your team needs to reach it from wherever they are working.
That is the decision qURL™ removes. None of those servers needs to answer the internet. They need to answer your people and your agents.
This isn't a new lesson for nginx, either. In 2025, IngressNightmare let an unauthenticated caller with network access to the ingress-nginx admission controller take over Kubernetes clusters. The webhook needed to accept requests from the Kubernetes API server, not arbitrary callers. Reachability is the vulnerability that keeps getting rediscovered.
How qURL Removes the Public Attack Path
The public attack path starts with a stranger connecting to nginx. qURL removes that step when you close every other public route to the origin.
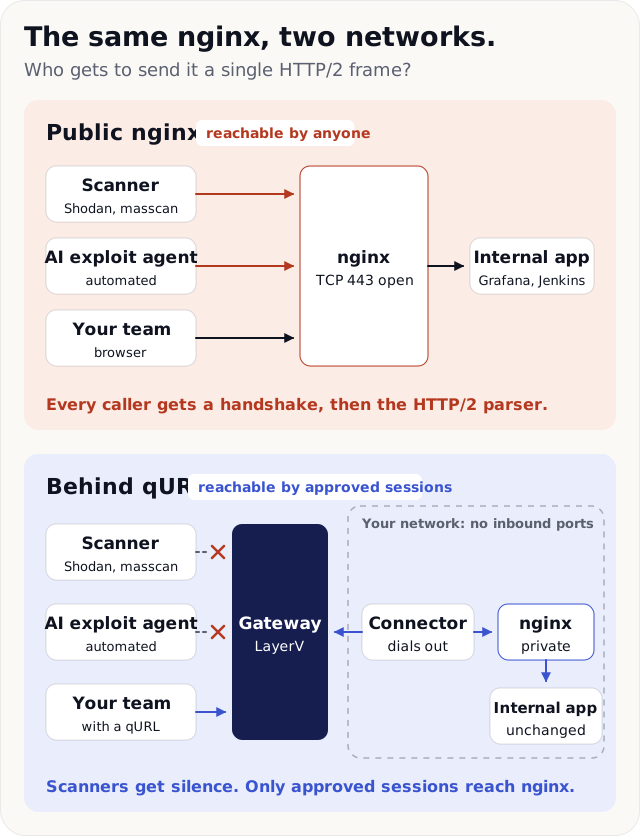
There is no listener to find. The qURL connector sits beside nginx and makes outbound connections only. Bind nginx to loopback and close every public path, including load balancers, other ingress and old origin addresses. Publishing a resource alone does not close these paths. AI scanners then have no app port to find or probe.
The gateway stays silent. In front of your resource is LayerV's gateway, built on OpenNHP, the network-hiding standard our team co-authored and the Cloud Security Alliance publishes. A caller without a valid, cryptographically authenticated knock gets nothing back: no banner, no error, nothing for a scanner to find. An exploit that needs to talk to an HTTP/2 parser has nobody to talk to.
Authorization comes before the connection. A qURL is a signed grant for one resource, with its own expiry and use limit. An invitation names a person, who verifies their email and saves a passkey. Either way, the gateway checks access before any traffic reaches the connector, and only that approved session ever touches nginx.
Remove the public foothold. The kernel bug needs code running on the host. Closing the public nginx route prevents unknown callers from using that route to reach the first stage. It does not fix either bug or prevent an approved recipient from attacking a reachable service. Standard access links are bearer credentials: protect them, limit their lifetime and revoke them when needed. Patch nginx and the kernel promptly.
You stop relying on the logs. Xint warns that CVE-2026-123007 leaves little evidence in access logs. With qURL, you are not trying to detect the attack in a log file afterward. You are preventing the connection that would have carried it.
Here's what a scanner sees on each side:
# Before: Grafana behind public nginx
$ curl -sI https://grafana.example.com
HTTP/2 302
server: nginx/1.31.8
location: /login

# After: nginx on loopback; all public ingress blocked by a dropping firewall
$ curl -sI --max-time 10 https://grafana.example.com
curl: (28) Connection timed out after 10001 milliseconds
The first response confirms a potential attack path: a live HTTP/2 listener and an exact, vulnerable version number. The second gives an attacker nothing to aim at.
Point nginx at loopback, then publish it and invite a recipient with the CLI:
# nginx now listens on 127.0.0.1:8080 instead of 0.0.0.0:443
qurl publish http://127.0.0.1:8080 --name "Internal Grafana" --access invite_only
qurl access invite <CRID> --email oncall@example.com
Your team keeps the same Grafana and the same SSO. The only thing that changes is who can open a connection.
Reduce Exposure While You Patch
nginx2root went from discovery to disclosure in 38 days. Your patch window started this morning, and a public proof of concept was on GitHub the same day.
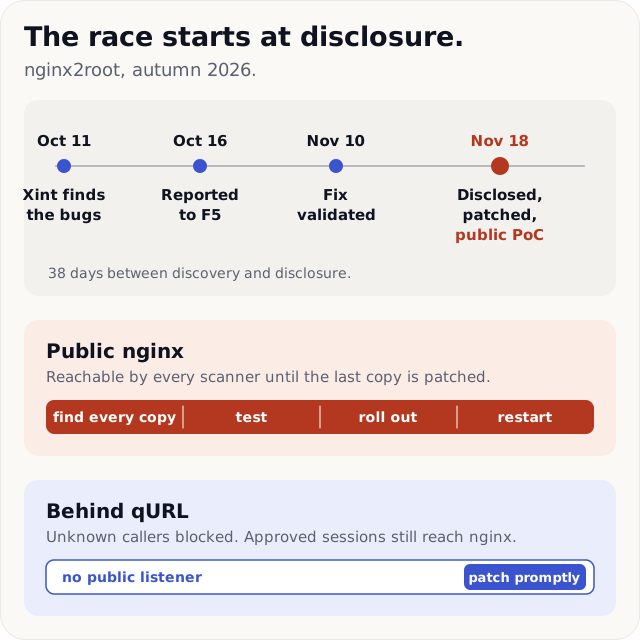
For public nginx, the next few days are a race. Find every copy, including the ones baked into images. Test the new build. Roll it out. Restart. Every hour in between, every scanner on the internet can try its luck.
Behind qURL, nginx has no public listener once all other ingress is closed. Only approved sessions can reach it. That reduces exposure while you test and deploy the patch; it does not justify waiting a week. That is preemptive security: remove access for unknown callers before they can send attack traffic.
Compare the Access Models
Access products differ in what they expose. Compare the public hostname, the origin listener and the policy that controls access.
| Approach | What a scanner finds | Who can send requests to the origin | On disclosure day |
|---|---|---|---|
| qURL | No app port once all other public ingress is closed; the NHP gateway ignores unauthenticated knocks | Only sessions with a valid qURL or invitation | Reduced public exposure; patch promptly |
| nginx on a public IP | Port 443 and a | Anyone on the internet | Emergency patch |
| VPN appliance | The appliance's own login portal | VPN users, after the appliance's own pre-auth code has run | Patch nginx and keep the VPN appliance patched too |
| Cloudflare Tunnel + Access (public hostname) | A public hostname and an Access login page | Users who pass the Access policy | Origin shielded; the gate itself stays public |
| Zscaler Private Access | Client mode: no app listener. Browser Access: a public hostname and a sign-in page | Users who pass the ZPA access policy | Origin shielded, once clients, app segments and policies are in place |
| Tailscale Funnel | A public ts.net hostname | Anyone on the internet | Emergency patch |
| ngrok | A public URL | Anyone with the URL, plus whatever auth you add | Emergency patch |
VPN appliances are public listeners with their own pre-auth parsers, and they keep proving it: Ivanti Connect Secure (CVE-2023-46805 and CVE-2024-21887), Fortinet's SSL VPN (CVE-2024-21762) and Palo Alto's GlobalProtect (CVE-2024-3400) were all exploited in the wild, several before a patch existed. Putting nginx behind one swaps one internet-facing parser for another. See LayerV vs VPN.
Cloudflare Tunnel with Access on a public hostname keeps the origin off the internet, which is the right instinct. But the hostname is in public DNS and the Access login page answers anyone who asks, so the gate is visible to every scanner. qURL's gate gives a scanner no reply at all, and it grants access per person or per link. See LayerV vs Cloudflare Access.
Zscaler Private Access uses outbound App Connectors too, then asks you to roll out Client Connector or configure Browser Access, define application segments and write access policies before the first user gets in. qURL publishes the internal tool and gives approved recipients a link that opens in a browser. See LayerV vs Zscaler Private Access.
Tailscale Funnel and ngrok solve the opposite problem. Funnel and ngrok public endpoints make a local service publicly reachable; added authentication changes who can reach the origin. Tailscale also has private sharing and Serve options, separate from Funnel. See LayerV vs Tailscale and qURL vs ngrok.
Start With the nginx You Wish You Didn't Have
Pick one internal tool behind nginx: the Grafana, the Jenkins, the staging site. Move nginx to loopback, publish it with qURL, invite the people who use it and close inbound 443. Check every public route and its firewall configuration, then scan the old addresses. One quiet scan does not prove all routes are closed.
Do it before the next disclosure. There will be one, and an AI will probably find it.
Take the Next Step
- Book a pilot — take your first internal nginx off the internet
- Hide internal applications — the full access workflow
- Quickstart — publish a private HTTP resource and send an invitation in minutes
nginx answers everyone. Make sure strangers can't reach it.